See your entire attack surface before attackers do.
NETEYES continuously discovers, monitors and secures every internet-facing asset you own — known and unknown — and catches threats before an attacker can. From one orbital command center.
24 modules · multi-tenant · MSSP-ready
You can’t protect what you can’t see
- Unknown attack surface
Shadow IT and forgotten infrastructure stay blind spots.
- Certificate surprises
An expired certificate is discovered through the outage.
- Exposed services
Open ports and orphaned databases sit exposed, unnoticed.
- Scattered tools
A separate screen and report for every client.
- Continuous discovery
Every internet-facing asset, known or unknown, is mapped.
- Certificate monitoring
Warns weeks before expiry, not after the outage.
- Evidence-based prioritization
You can say why this one comes first.
- One command center
Dozens of isolated clients managed from one panel.
Built to catch what others miss
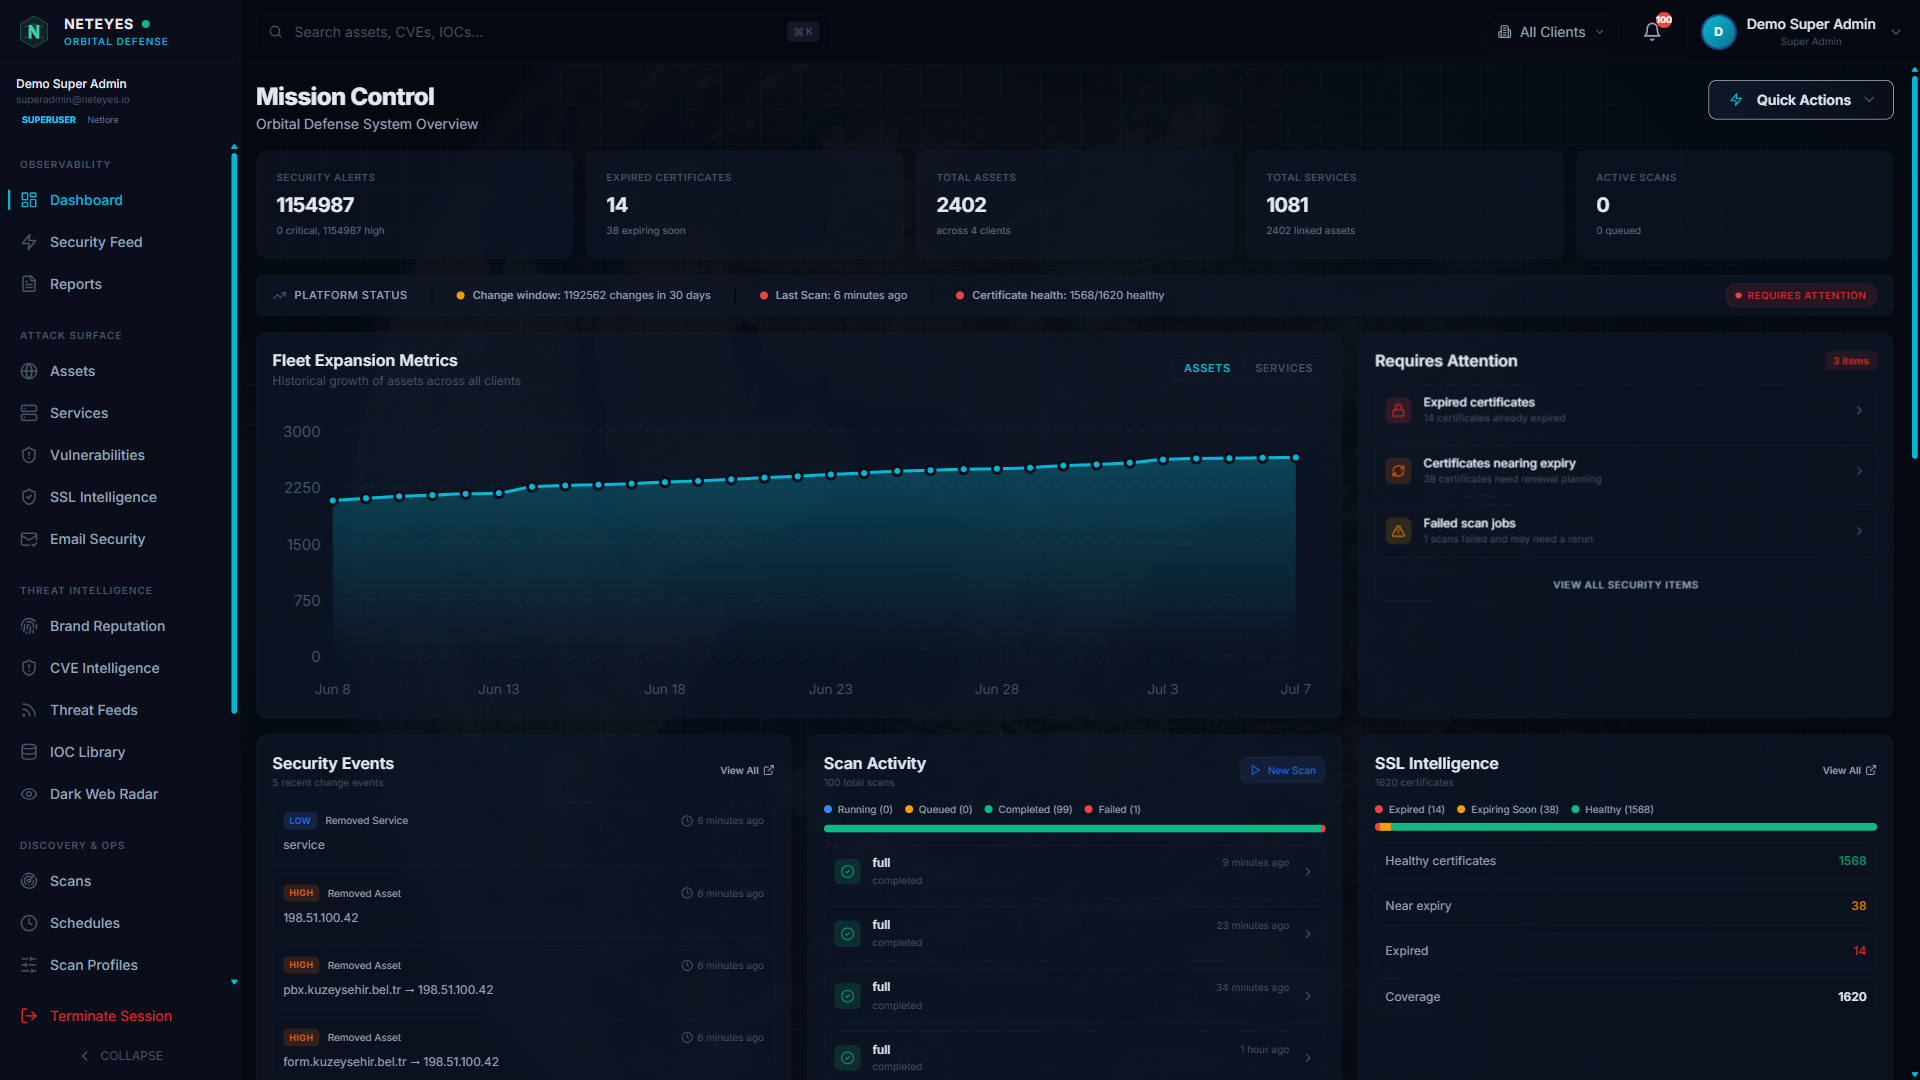
Mission Control Dashboard
Your entire attack surface on one screen — see what’s on fire without looking away.
- Five critical KPI cards — critical/high alerts, expired certificates, total assets & services and live scans — each one-click deep-links to detail.
- Composite Risk Score (A–F) — a single enterprise grade rolled up from per-asset risk, showing the weighted factors driving it.
- Smart “Needs Attention” panel and Top Riskiest Assets ranking route expiring certs, critical changes and failed scans straight to the fix.
- Multi-tenant superadmin view — every client’s assets, services and growth plus Sentinel fleet health in one panel.
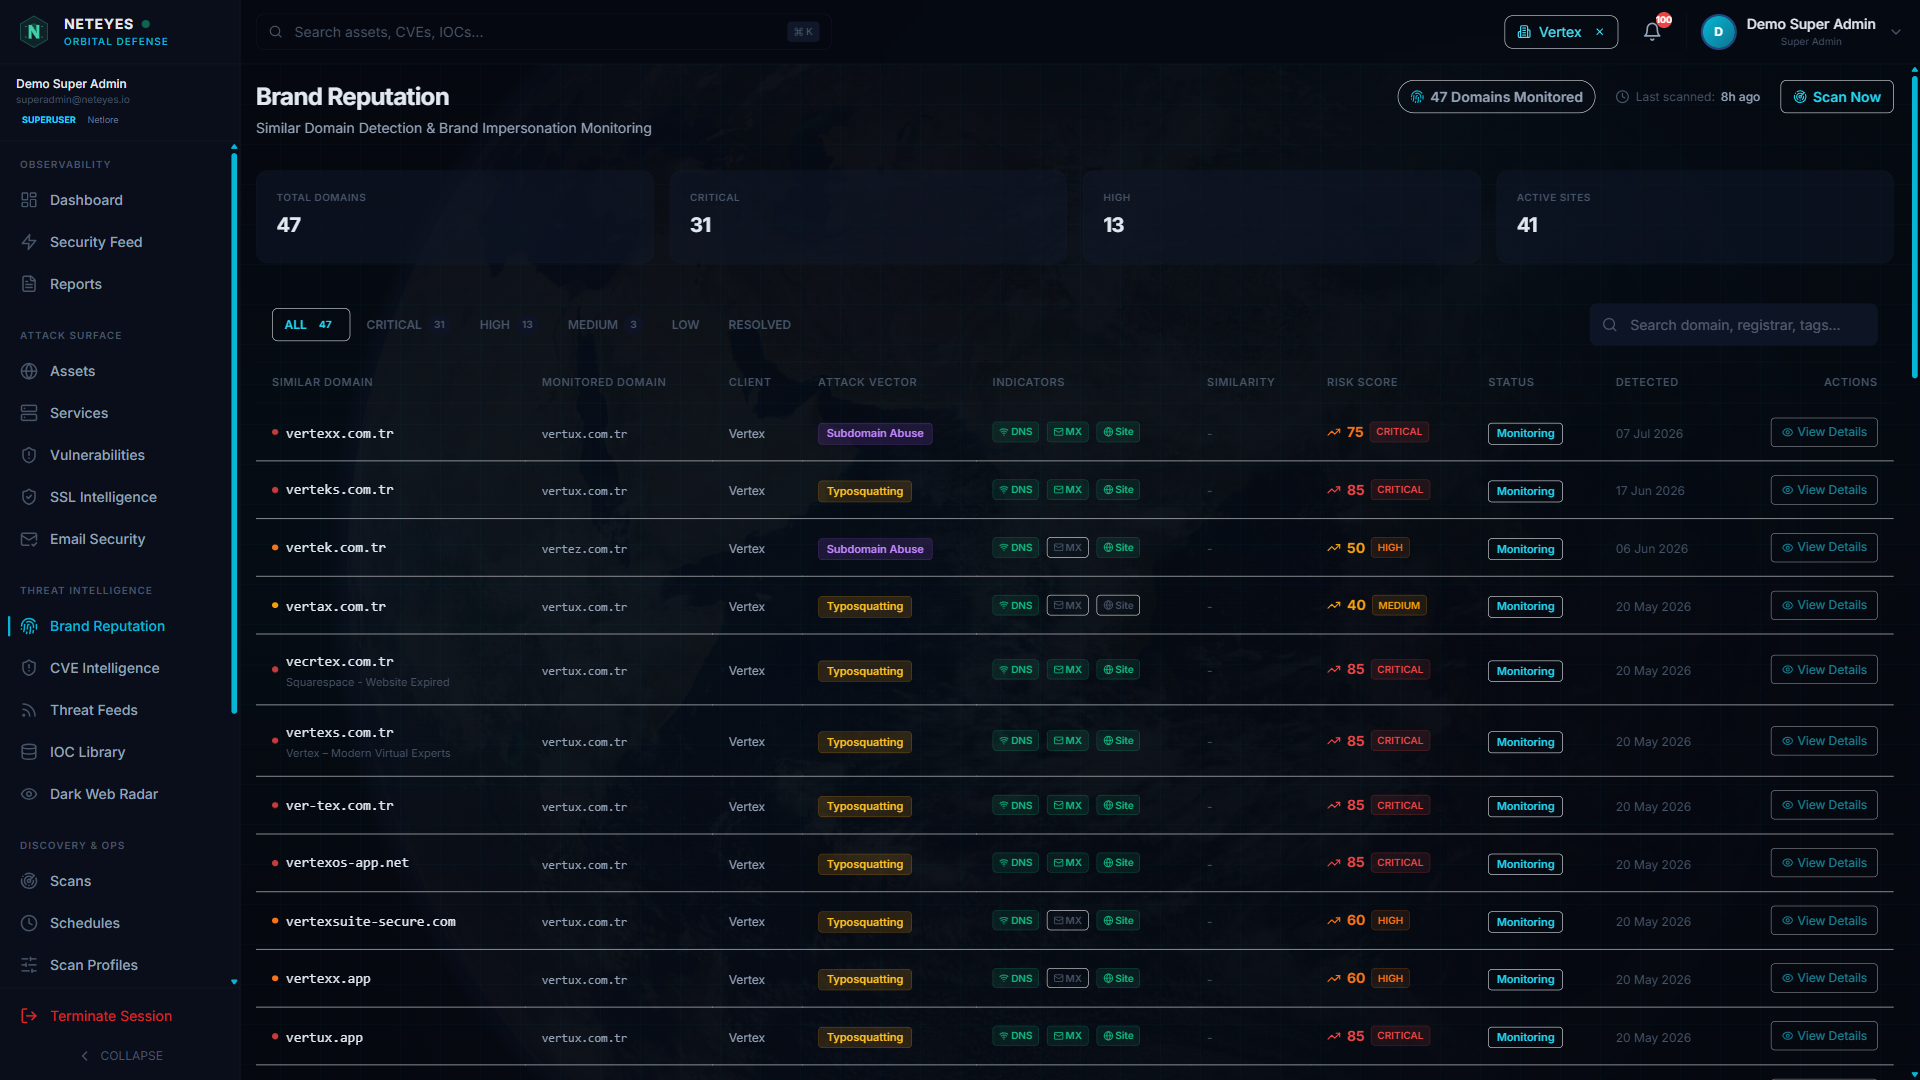
Brand & Lookalike Domain Radar
Catch every fake domain impersonating your brand before it casts its first hook.
- Five attack-vector classifications — Typosquatting, Homoglyph, TLD Variation, Subdomain Abuse and Brand Impersonation; know instantly which technique you face.
- 0–100 smart risk score + live threat indicators (DNS/MX/Site) and visual-similarity % — can the fake send email, is a site live, how closely does it copy yours.
- End-to-end takedown workflow — tracks each domain’s shutdown through a “Requested → In progress → Removed” lifecycle.
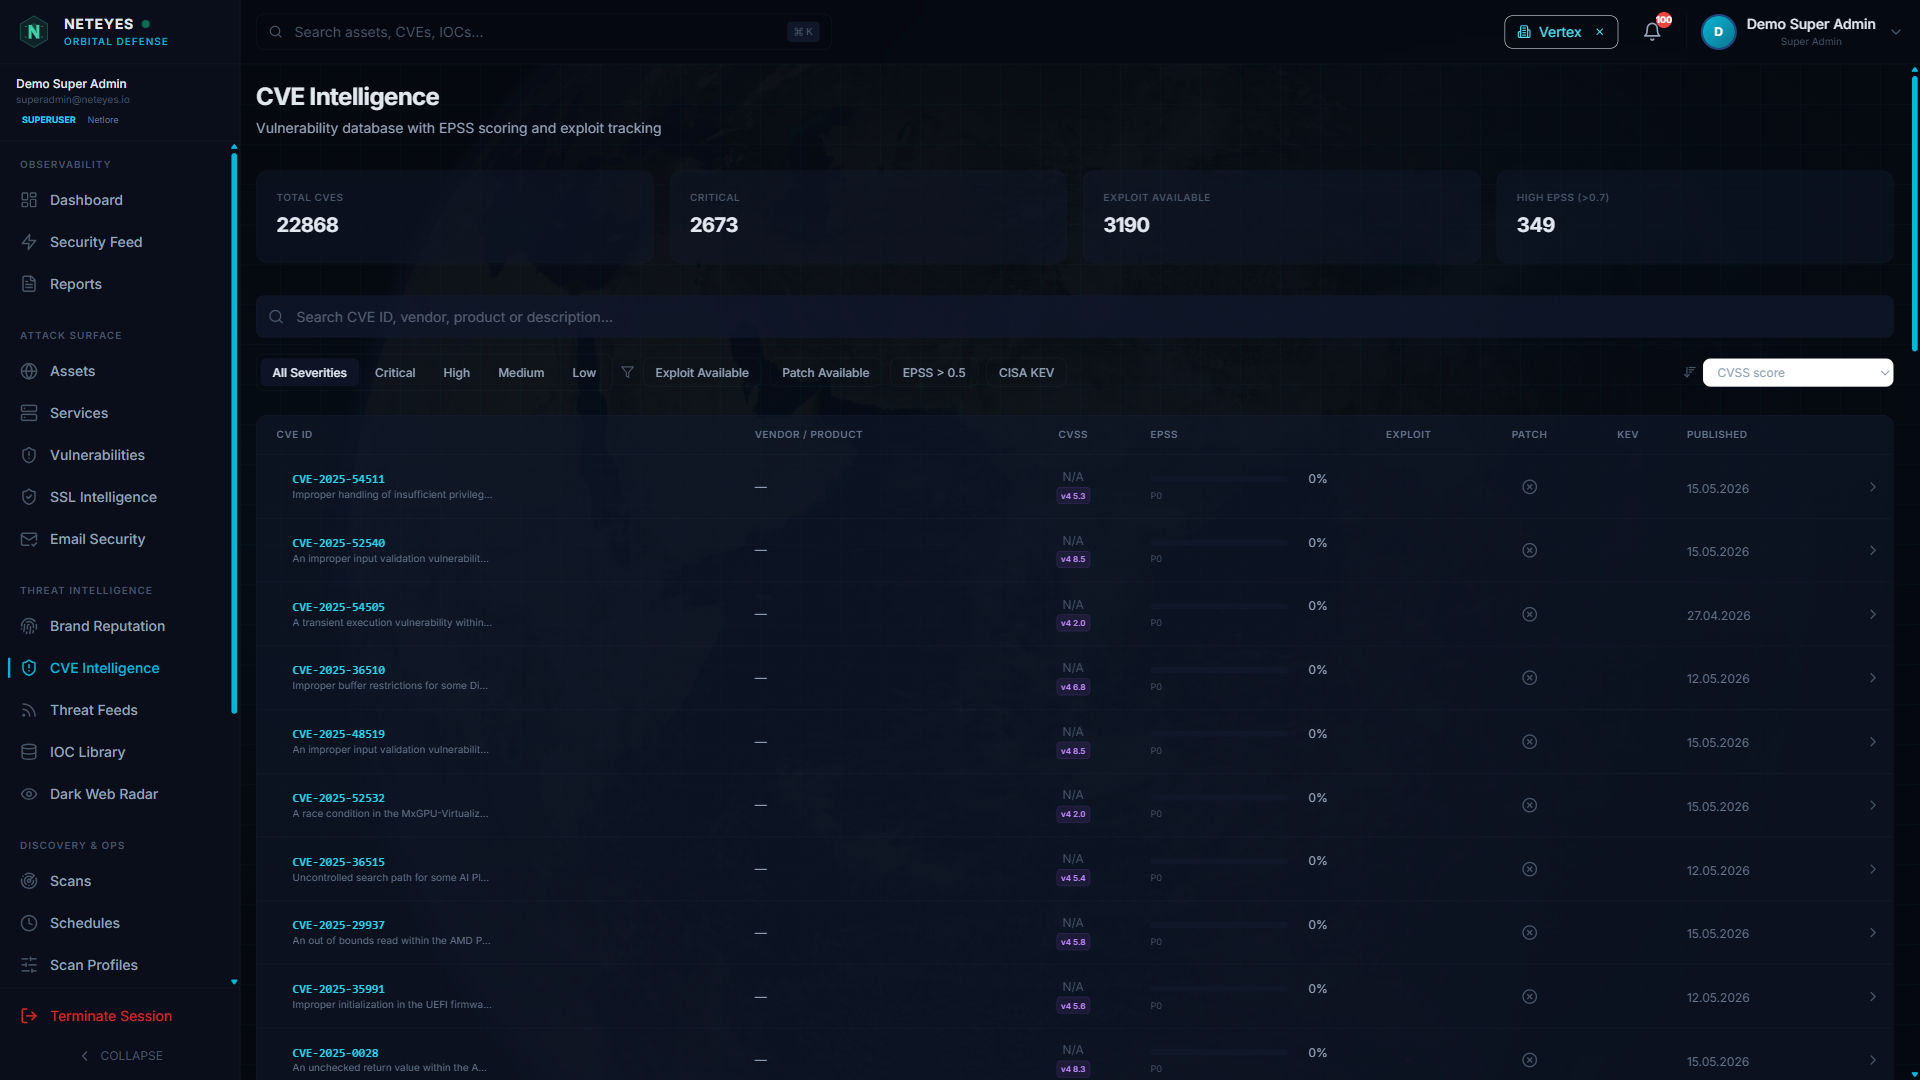
CVE Intelligence
Find the one vulnerability that will actually hit you — in seconds, among thousands.
- NVD + EPSS + CISA KEV fusion — CVSS v3/v4, EPSS probability/percentile and the KEV list side by side in one table.
- Smart priority ranking and tri-state filters — surfaces “most likely to be exploited”; chain exploit/patch/high-EPSS/KEV filters as include/exclude/off.
- Vulnerabilities that touch YOU — an affected-assets table links discovered services to the CVE via CPE match, with port, protocol and a version-confirmed badge.
Security teams that demand visibility
Whether you protect one organization or hundreds, NETEYES scales to meet you.
See your external surface for the first time — automatic discovery, continuous scanning and a live dashboard, out of the box.
Full-surface visibility with evidence-based prioritization, deep threat intelligence and native SIEM/SOAR integration.
Manage dozens of fully isolated clients from one panel — multi-tenant onboarding, per-client licensing and a distributed sentinel fleet.
- 24
- modules, one platform
- 0–65535
- full-spectrum port scanning
- 24/7
- continuous monitoring
- A–F
- composite risk grading
Scales from a small team to an MSSP
Three plans, modular by design. Start with visibility, add threat-intelligence modules à la carte as you grow.
Professional
Full threat intelligence for a mature security team.
View pricingReady to eliminate your blind spots?
Join the security teams who trust NETEYES for complete external attack surface visibility. Book a demo and see your own surface, live.